

Sourcery
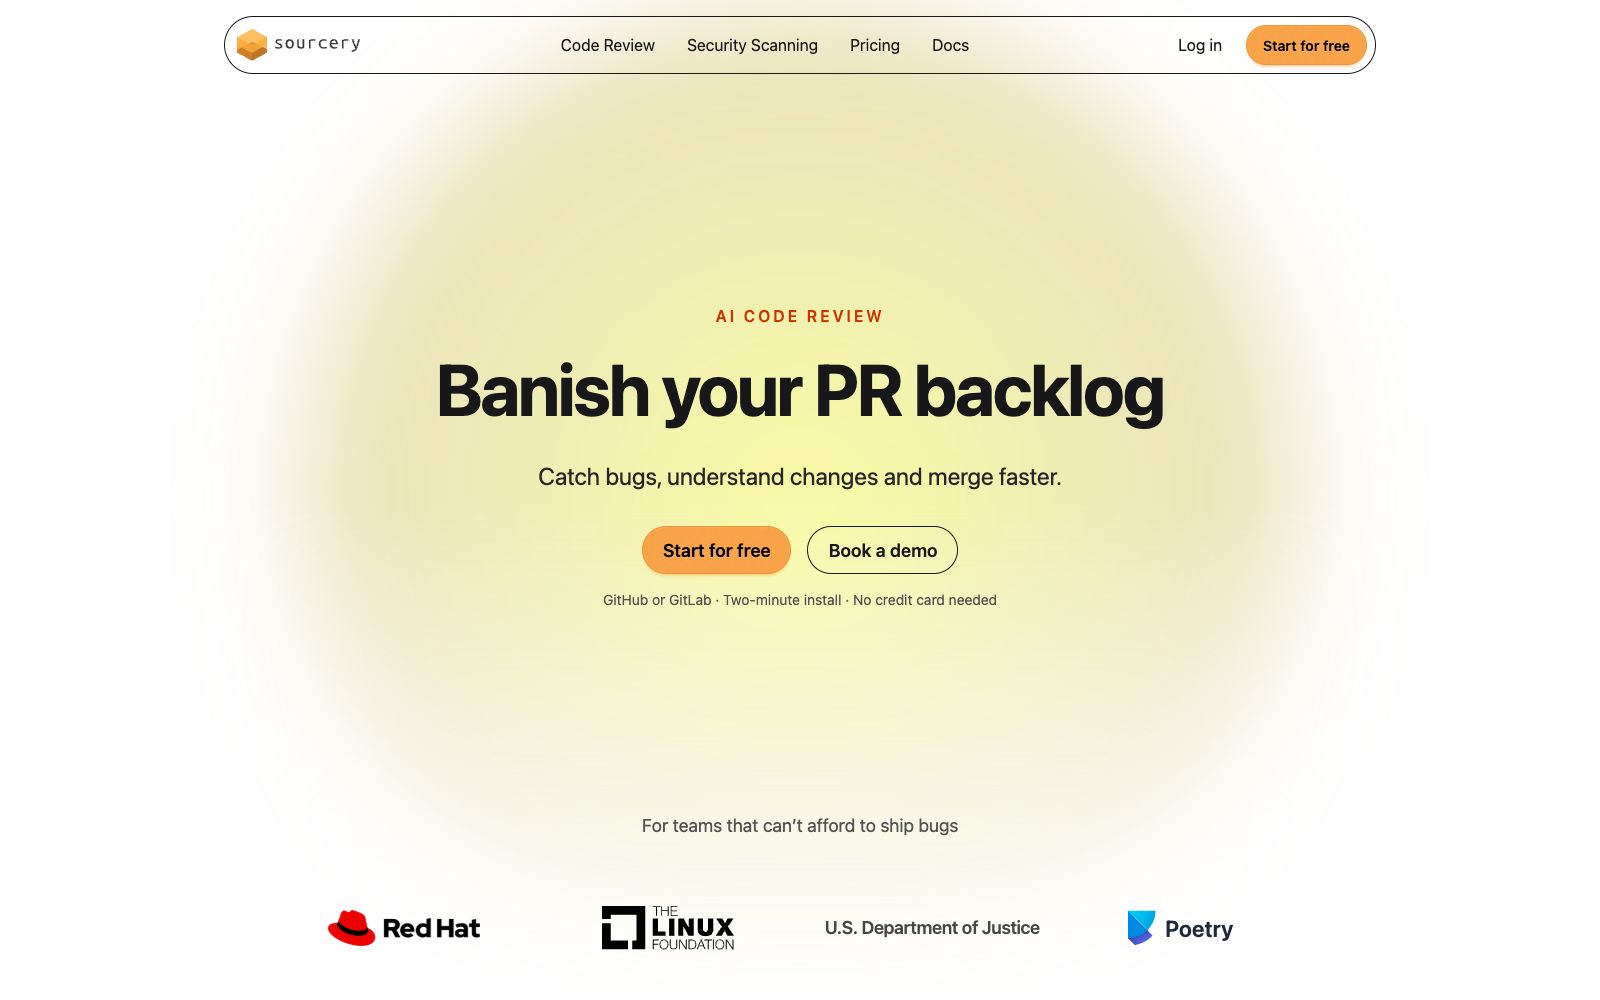
Sourcery is a team-oriented AI code review tool. After integrating with GitHub and GitLab, it automatically reviews every pull request, detects defects, scans for security vulnerabilities, and provides one-click repair suggestions.
Updated: 2026-10-26
What is Sourcery?
Sourcery is an AI-powered code review tool for teams. After integrating with GitHub and GitLab, it automatically reviews every pull request within minutes. It can detect logical flaws, missing edge cases, and scan for security vulnerabilities, clearly explaining issues and providing one-click adoptable fix suggestions. For teams that don't want slow merge progress due to trivial issues, it acts as a permanent code review assistant, freeing humans from repetitive code checks.
Who is it for?
- Teams maintaining open-source projects: The open-source version is free, making it ideal for maintainers who receive frequent community contributions and need to quickly assess the quality of PRs.
- R&D teams with fast engineering cycles: Medium-to-large technical teams that aim to reduce review backlogs and speed up the merging process.
- Teams using GitHub or GitLab: Installation takes two minutes, no credit card required to get started, with very low onboarding threshold.
- Teams integrating coding agents: When part of the code is generated by AI, Sourcery can be used to uniformly review the changes made by humans and AI agents.
- Organizations focused on code security: Treat security scan results as a mandatory check before merging to reduce the inflow of faulty code into the main branch.
Key features
5Automated review for every commit: After integrating with GitHub or GitLab, Sourcery completes the review within minutes, automatically releasing PR summaries, review comments and repair suggestions, eliminating the need for manual queuing.
Defect and Security Scanning
It detects logical errors, overlooked edge cases, and security issues in the code, explains the causes of the problems and how to fix them, and enables developers to quickly identify risk points.
One-click adoption of fixes
For detected defects, Sourcery formulates the fixes as suggested changes, which developers can directly commit to the PR, eliminating the need for repetitive copy-pasting when modifying code manually.
Change Summary
The PR summary will indicate what has been changed and which areas to focus on, enabling quick understanding of the intent regardless of whether the code comes from colleagues or coding agents.
Auto-approval for low-risk changes: For low-risk PRs with no blocking issues, Sourcery can approve them directly, and they can be merged after the CI passes, freeing up manual review bandwidth for complex changes.
How to use Sourcery
- 1Try it on open-source repositories first: The free plan covers public projects, so you can validate the effect on small repositories before rolling it out to internal codebases.
- 2Focus on the summary rather than line-by-line: During reviews, prioritize reading the PR summary and focus your energy on the key areas and risk items marked by Sourcery.
- 3Handle by risk level: Enable auto-approval for PRs marked as low-risk, and leave manual reviews for truly complex business logic changes.
- 4Integrate security checks into the workflow: Treat the results of security scans as a mandatory check before merging. Roll back vulnerabilities in a timely manner or require additional testing when they are discovered.
- 5Use with CI: Link auto-approval to CI results to ensure that merging into the main branch is only allowed when tests pass and there are no blocking issues.
Traffic & popularity
Data month Sep 2026
Sourcery receives about 12.5K visits per month and ranks #2,292,610 worldwide.
Monthly visits
12 monthsTraffic sources
- Direct57.6%
- Search22.5%
- Referrals9.2%
- Social6.7%
- Mail2.4%
- Other1.7%
Top countries
- Sweden14.0%
- United States11.1%
- India6.6%
- Netherlands6.1%
- Spain5.7%
Estimated from third-party traffic data.
Similar tools
 QodoAn AI platform for code review provides cross-repository context and more than 15 agent workflows, covers IDE, PR and security scenarios, and transforms team specifications into executable governance rules.
 CodeRabbitCodeRabbit is an AI-first Pull Request review tool that provides line-by-line contextual suggestions before code merging, automatically sorts review priorities, and monitors security vulnerabilities, enabling teams to deliver more stable code faster.
 Claude CodeAnthropic's programming agent tool can read the entire codebase, directly modify files and run commands. It can take on the entire work of defect repair and cross-day migration. Terminals, editors, chat software and web pages are all its entry points.
 OpenHandsOpenHands is an open-source cloud-based coding intelligent agent platform. It is model-agnostic, can automatically turn engineering requests into deployable changes, and integrates with Slack, GitHub, and Jira to handle reviews, triage, and security scanning.
 MonkeyCodeOnline AI programming platform, officially available for free use with unlimited quota. It comes with a cloud development environment and terminal, file management, and port preview, and links projects, requirements, and Git Review in the same workflow.
 MacroscopeAn AI code review tool for R&D teams that checks the correctness, security, testing and regression risks of each change before merging, automatically generates PR descriptions and summarizes multi-repository changes, and also includes a cloud-based coding Agent.