Zof
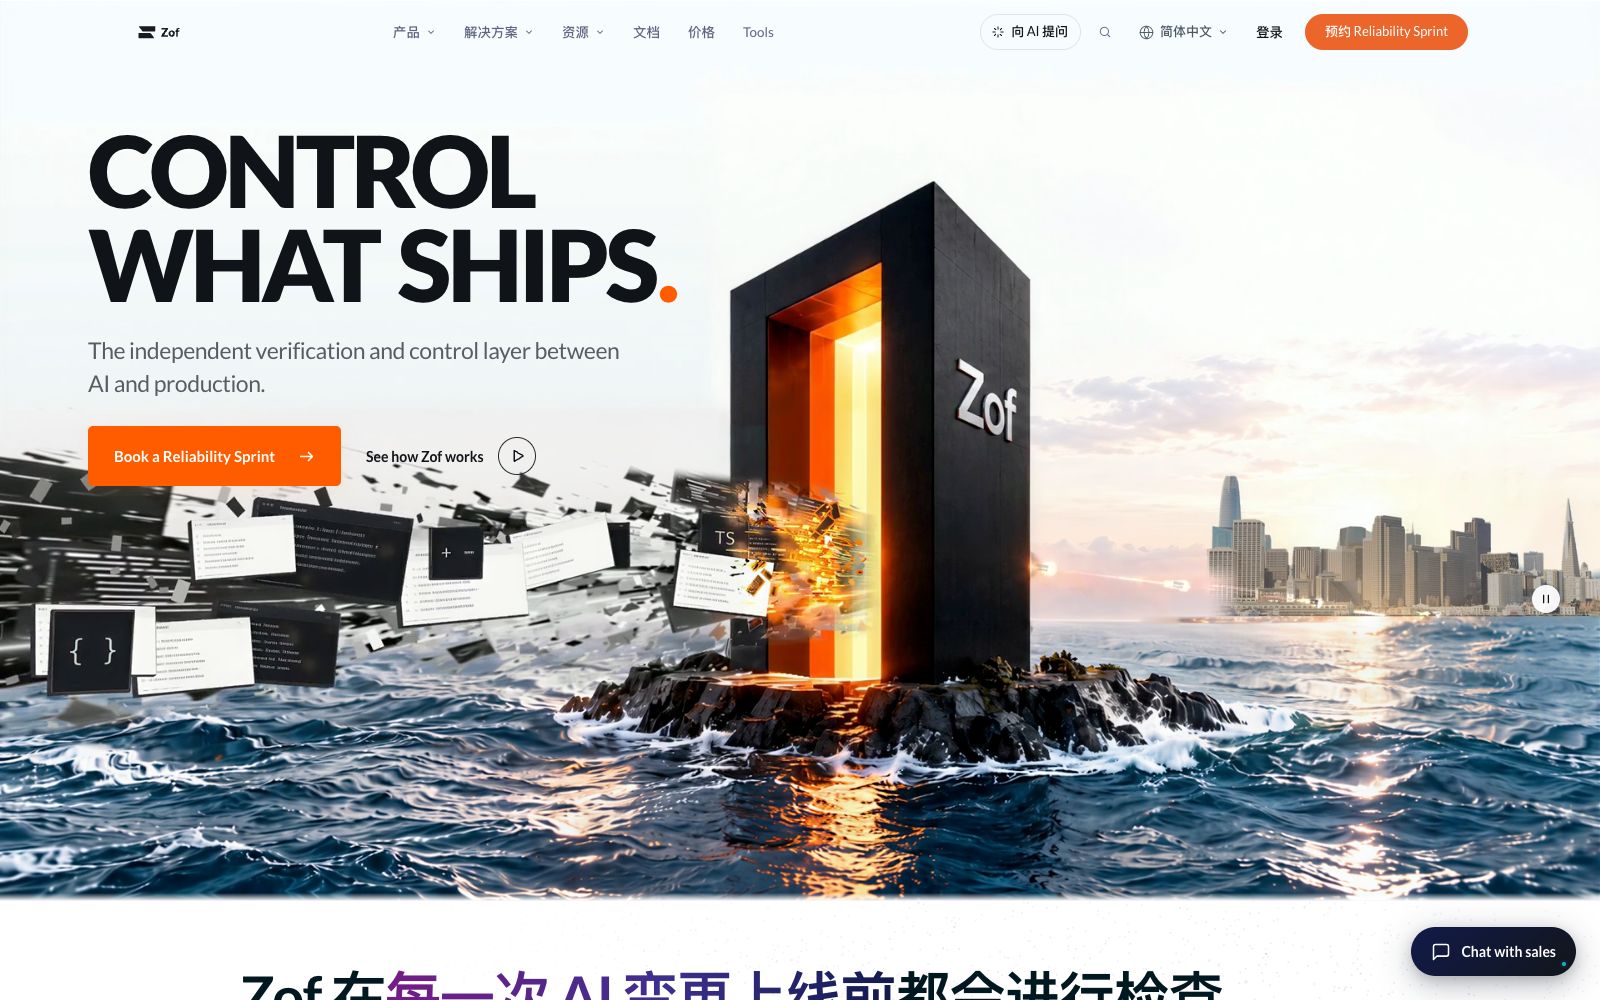
Zof is an independent verification and control layer located between AI and production environments. According to its official website, after the changes generated by AI arrive, Zof first judges the possible scope of impact, then runs unit tests, security and compliance checks and leaves evidence, and finally decides to allow, block or transfer to manual approval through strategies. It covers scenarios such as output from coding agents, release review and audit forensics.
Updated: 2026-10-26
What is Zof?
Zof's official website positions itself as "an independent verification and control layer between AI and production environments". Its difference from conventional CI or testing platforms lies in its stance: in the official demo, when a change from a coding agent arrives, "nothing is trusted". It first judges what the change may affect, then runs appropriate checks and leaves records, and finally your rules decide whether to allow it, block it, or route it to manual approval. The sample change in the official demo is a PR modifying the payment login code, which is treated as untrusted until the check is completed.
Who is it for?
- Engineering leaders who have coding agents directly producing PRs and need an independent check to be added before merging
- SRE teams that want to understand the scope of impact before changes go live, rather than waiting for alerts to trigger
- QA leaders who want testing to become evidence rather than a long-term maintenance burden
- CTOs who need to provide exportable evidence for the board of directors or external audits, as well as security and compliance teams
- Teams responsible for production releases in regulated industries such as financial services, healthcare, SaaS, and B2B
Key features
6System Graph
The official website states that it is a real-time map of your services, data, responsible persons and history, allowing the consequences of a change to be known before it is executed, and answering "what will a change break?".
Verification Engine
According to the official website, this component determines what proof is required for each change and verifies it. Its scope ranges from unit tests to security, load, and compliance checks, with a record kept for each inspection.
Evidence Retention
It is stated on the official website that it will permanently store what has been modified, what has been verified, and who has approved it, which can be directly used for release reviews and audits, and delivered as an exportable evidence package.
Control & Strategy
The official website states that your policies determine whether to allow, block, or require approval from designated personnel, and this is enforced where the action takes place, not just recommended; approval rules, change windows, and rollback paths are first-class citizens of the control plane.
Identity & Audit
The official website states that every operation is bound to a named identity via RBAC and SSO, with no shared credentials; every detection, approval, and repair is recorded as type-specific, exportable evidence.
On-Premises Deployment
The official website states that Zof can be deployed in your cloud, VPC, on-premises data center, or isolated network, offering a zero-data retention option where your code never leaves your environment.
How to use Zof
- The official website offers two entry points: a free trial, and a paid Reliability Sprint for a critical system (the website states it will usually identify where the problems are, why they occur, and what is reliable within seven days).
- if you are unsure about its suitability, book a 30-minute demo first.
- Determine the deployment mode before integration: The official website supports self-owned cloud, VPC, on-premises and isolated networks, and provides a zero-data-retention option.
- The network boundaries and egress policies should be clarified during the selection phase.
- Align permissions and compliance with the four points on the official website: identity first (RBAC plus SSO, no shared credentials), default auditing, staying within your perimeter, and decision-making by strategy.
- formalize approval rules and change windows into policies instead of scattering them across pipeline scripts.
- Run it first on a system where you can define the scope of failures, and at the same time complete the service, data, and responsible person information required by the System Graph.
- otherwise, there will be a lack of data for impact assessment.
- Treat it as an overlay rather than a replacement: The official website states that there is no need to replace anything, but you need to clarify which repositories, CI and deployment systems it reads from and grant permissions in accordance with the principle of least privilege.
Traffic & popularity
Data month Sep 2026
Zof receives about 71.8K visits per month and ranks #424,692 worldwide.
Monthly visits
12 monthsTraffic sources
- Social49.8%
- Direct32.0%
- Search9.3%
- Referrals6.0%
- Mail3.0%
Top countries
- United States57.0%
- Ghana34.9%
- India3.8%
- Indonesia2.7%
- Bangladesh1.4%
Estimated from third-party traffic data.